[Sep 03, 2025] CAS-005 Exam Dumps 100% Same Q&A In Your Real Exam [Q64-Q85]

4.5/5 - (24 votes)

[Sep 03, 2025] CAS-005 Exam Dumps 100% Same Q&A In Your Real Exam

CAS-005 Test Engine Dumps Training With 219 Questions

CompTIA CAS-005 Exam Syllabus Topics:

Topic Details
Topic 1
  • Security Engineering: This section measures the skills of CompTIA security architects that involve troubleshooting common issues related to identity and access management (IAM) components within an enterprise environment. Candidates will analyze requirements to enhance endpoint and server security while implementing hardware security technologies. This domain also emphasizes the importance of advanced cryptographic concepts in securing systems.
Topic 2
  • Governance, Risk, and Compliance: This section of the exam measures the skills of CompTIA security architects that cover the implementation of governance components based on organizational security requirements, including developing policies, procedures, and standards. Candidates will learn about managing security programs, including awareness training on phishing and social engineering.
Topic 3
  • Security Architecture: This domain focuses on analyzing requirements to design resilient systems, including the configuration of firewalls and intrusion detection systems.
Topic 4
  • Security Operations: This domain is designed for CompTIA security architects and covers analyzing data to support monitoring and response activities, as well as assessing vulnerabilities and recommending solutions to reduce attack surfaces. Candidates will apply threat-hunting techniques and utilize threat intelligence concepts to enhance operational security.


Q64. A security analyst is reviewing the following event timeline from an COR solution:

Which of the following most likely has occurred and needs to be fixed?


Q65. An organization is developing a disaster recovery plan that requires data to be backed up and available ata moment’s notice. Which of the following should the organization consider first to address this requirement?


Q66. A security engineer needs to review the configurations of several devices on the network to meet the following requirements:
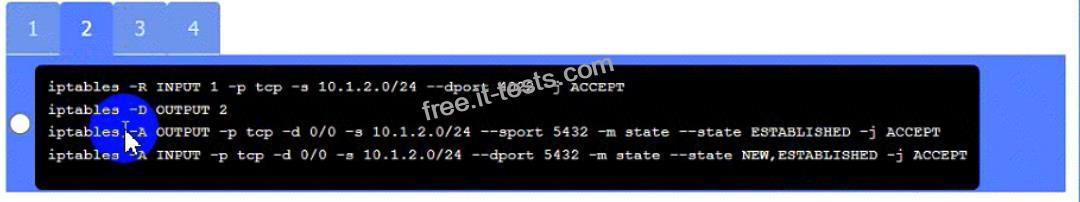
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24 subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
* All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh

WAP A

PC A

Laptop A

Switch A

Switch B:

Laptop B

PC B

PC C

Server A


Q67. You are a security analyst tasked with interpreting an Nmap scan output from company’s privileged network.
The company’s hardening guidelines indicate the following:
There should be one primary server or service per device.
Only default ports should be used.
Non-secure protocols should be disabled.
INSTRUCTIONS
Using the Nmap output, identify the devices on the network and their roles, and any open ports that should be closed.
For each device found by Nmap, add a device entry to the Devices Discovered list, with the following information:
The IP address of the device
The primary server or service of the device (Note that each IP should by associated with one service/port only) The protocol(s) that should be disabled based on the hardening guidelines (Note that multiple ports may need to be closed to comply with the hardening guidelines) If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

Q68. A security analyst is reviewing the following log:

Which of the following possible events should the security analyst investigate further?


Q69. A mobile device hardware manufacturer receives the following requirements from a company that wants to produce and sell a new mobile platform:
– The platform should store biometric data.
– The platform should prevent unapproved firmware from being loaded.
– A tamper-resistant, hardware-based counter should track if unapproved firmware was loaded.
Which of the following should the hardware manufacturer implement? (Select three).


Q70. During a security assessment using an CDR solution, a security engineer generates the following report about the assets in me system:

After five days, the EDR console reports an infection on the host 0WIN23 by a remote access Trojan Which of the following is the most probable cause of the infection?


Q71. A company lined an email service provider called my-email.com to deliver company emails. The company stalled having several issues during the migration. A security engineer is troubleshooting and observes the following configuration snippet:

Which of the following should the security engineer modify to fix the issue? (Select two).


Q72. A systems engineer is configuring a system baseline for servers that will provide email services. As part of the architecture design, the engineer needs to improve performance of the systems by using an access vector cache, facilitating mandatory access control and protecting against:
* Unauthorized reading and modification of data and programs
* Bypassing application security mechanisms
* Privilege escalation
* interference with other processes
Which of the following is the most appropriate for the engineer to deploy?


Q73. A security officer performs due diligence activities before implementing a third-party solution into the enterprise environment. The security officer needs evidence from the third party that a data subject access request handling process is in place. Which of the following is the security officer most likely seeking to maintain compliance?


Q74. A security architect is implementing more restrictive policies to improve secure coding practices.
Which of the following solutions are the best ways to improve the security coding practices?
(Choose two.)


Q75. A global organization wants to manage all endpoint and user telemetry. The organization also needs to differentiate this data based on which office it is correlated to. Which of the following strategies best aligns with this goal?


Q76. SIMULATION
[Security Architecture]
An organization is planning for disaster recovery and continuity ofoperations, and has noted the following relevant findings:
1. A natural disaster may disrupt operations at Site A, which would then cause an evacuation. Users are unable to log into the domain from-their workstations after relocating to Site B.
2. A natural disaster may disrupt operations at Site A, which would then cause the pump room at Site B to become inoperable.
3. A natural disaster may disrupt operations at Site A, which would then cause unreliable internet connectivity at Site B due to route flapping.
INSTRUCTIONS
Match each relevant finding to the affected host by clicking on the host name and selecting the appropriate number.
For findings 1 and 2, select the items that should be replicated to Site B. For finding 3, select the item requiring configuration changes, then select the appropriate corrective action from the drop-down menu.

Q77. An organization wants to create a threat model to identity vulnerabilities in its infrastructure.
Which of the following, should be prioritized first?


Q78. A security analyst reviews the following report:

Which of the following assessments is the analyst performing?


Q79. Which of the following best describes the reason a network architect would enable forward secrecy on all VPN tunnels?


Q80. A company lined an email service provider called my-email.com to deliver company emails. The company stalled having several issues during the migration. A security engineer is troubleshooting and observes the following configuration snippet:

Which of the following should the security engineer modify to fix the issue? (Select two).


Q81. An audit finding reveals that a legacy platform has not retained loops for more than 30 days. The platform has been segmented due to its interoperability with newer technology. As a temporary solution, the IT department changed the log retention to 120 days. Which of the following should the security engineer do to ensure the logs are being properly retained?


Q82. A company’s SIEM is continuously reporting false positives and false negatives. The security operations team has implemented configuration changes to troubleshoot possible reporting errors. Which of the following sources of information best supports the required analysis process?
(Choose two.)


Q83. During a recent security event, access from the non-production environment to the production environment enabled unauthorized users to:
* Install unapproved software
* Make unplanned configuration changes
During the investigation, the following findings were identified:
* Several new users were added in bulk by the IAM team
* Additional firewalls and routers were recently added
* Vulnerability assessments have been disabled for more than 30 days
* The application allow list has not been modified in two weeks
* Logs were unavailable for various types of traffic
* Endpoints have not been patched in over ten days
Which of the following actions would most likely need to be taken to ensure proper monitoring? (Select two)


Q84. An audit finding reveals that a legacy platform has not retained loos for more than 30 days The platform has been segmented due to its interoperability with newer technology. As a temporary solution, the IT department changed the log retention to 120 days. Which of the following should the security engineer do to ensure the logs are being properly retained?


Q85. A company updates its cloud-based services by saving infrastructure code in a remote repository. The code is automatically deployed into the development environment every time the code is saved lo the repository The developers express concern that the deployment often fails, citing minor code issues and occasional security control check failures in the development environment Which of the following should a security engineer recommend to reduce the deployment failures? (Select two).


CAS-005 Practice Test Pdf Exam Material: https://www.it-tests.com/CAS-005.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw